
I run a small Windows system at home around the clock and reach it remotely by RDP from a laptop, tablet or smartphone. Repeated unauthorized connection attempts made me reconsider exposing RDP directly. I previously described RDP over SSH; it works, but the TCP tunnel has limits. In this July 2021 experiment, I tried a more flexible alternative based on WireGuard VPN. Here were the options I considered:
- RDP over SSH tunneling. OpenSSH client and server became optional features in Windows 10 build 1809, as described in the previous post. After using this setup, I found these limits:
- My iPhone setup lacked an RDP client with integrated SSH forwarding, and keeping a separate SSH session alive in the background was unreliable. iOS background behavior depends on the app and mode; there is no universal 30-second limit for every SSH client.
- The
ssh -Ltunnel carries TCP, while RDP can also use UDP. - After some Windows updates, I found the OpenSSH service stopped or disabled. I did not determine the cause.
- Install VPN on the home router. My router supports both WireGuard and OpenVPN, but I preferred not to add another service to a critical network device. Firmware updates and configuration also need attention.
- Put a Raspberry Pi on the home network as a VPN server. I use several Raspberry Pi 4 systems, and in my 2021 gigabit-network test one handled around 300 Mbps of WireGuard traffic. That is a historical measurement on my setup, not a throughput guarantee.
- Run a Linux VPN server in a Hyper-V virtual machine on Windows. This is possible, but it adds a VM and recovery work after power loss or host updates; I preferred a simpler host setup.
- Install a VPN server directly on Windows. I had been working with WireGuard for several years, so it was the natural choice for this experiment.
Preliminary research
By July 2021, WireGuard was in the mainline Linux kernel, while the official Windows client I was using still relied on a Go implementation. Its tunnel service could also run a peer that accepts connections, so it was suitable for the server side of this setup. Henry Chang described a Windows setup, and micahmo automated some of those steps. I had not tested micahmo’s application when I wrote this. A comment under Henry’s post raised a useful requirement:
Good day, excellent article!
I have a Win10 machine that I plan to use as a wireguard server. This machine has a main internet network adapter + OpenVPN client connection that is used for selected routes.
If I understand correctly described above wireguard VPN setup will only allow my wireguard clients to access main internet interface but not the OpenVPN connection, please correct me I’m wrong.
Is there a way for a wireguard client to use all available connections and honor existing routes configuration on wireguard server?Thank you!
The commenter wanted WireGuard clients to reach destinations through the gateway host’s existing routes, including a selected OpenVPN connection. Windows Internet Connection Sharing shares a selected public connection; this experiment also needed gateway-originated proxy connections to follow the host’s routing choices. That shaped the requirements below.
Requirements
- Simplify the process of installing and configuring WireGuard as much as possible. The pressure on companies providing VPN services is growing, and we never know what really happens with our data, so I wanted a Windows user to be able to:
- Easily install the WireGuard VPN Server on a cloud hosted VPS without diving into implementation specifics. It could be useful to bypass geographic restrictions on some online products or services. For example, I found the Ghidra website inaccessible from an IP address in Russia in 2021, while its binaries were available on GitHub. Airline sites also showed me different fares or currencies by location; those prices can change for many reasons.
- Easily install WireGuard VPN Server on a home Windows machine to reach home TCP and UDP services from networks that can reach the server, subject to the host and network firewall rules.
- Propose some kind of Internet Connection Sharing alternative which would use all available connections and honor existing routes.
I started working on this project about a month before publishing this July 2021 article. By then, I had it running on two home machines with Windows 10 Pro and one Microsoft Azure VPS (Windows Server 2019 Core, 1 vCPU and 1 GB RAM). Linux was already an established WireGuard server option; my goal here was a simpler path for Windows users. The most difficult setup step was forwarding the chosen UDP port on a home router or allowing it through a VPS firewall.
WireSock VPN Gateway
Choosing the project name was not easy, but WireSock was close to WireGuard, and WireSock.net was available. After installing WireSock VPN Gateway, run wg-quick-config -add -start from an elevated shell on the gateway host. The generator prompts for a WireGuard IPv4 subnet (suggesting 10.9.0.0/24 for a fresh setup), detects an external address and an available local UDP port, and lets you enter a hostname and port instead. Verify the endpoint and choose a subnet that does not overlap either side’s network. On a home router or VPS firewall, allow and forward the chosen UDP port as required; a public address or host name alone does not configure that path.
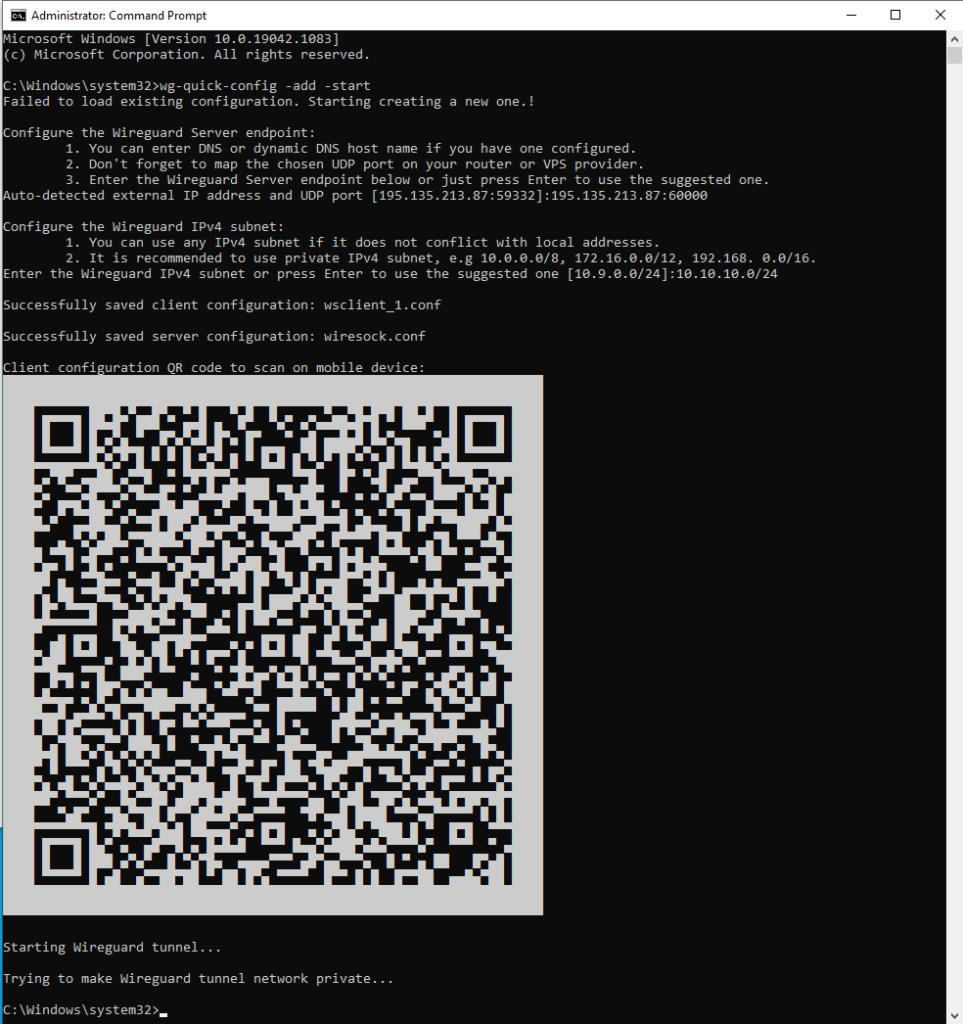
wg-quick-config creates configuration files for the server (wiresock.conf) and client (wsclient_1.conf), after that, it creates and launches the WireGuard tunnel. It also displays the client configuration as a QR code that can be scanned by a smartphone. Additional clients can be added by calling ‘wg-quick-config -add -restart’.
wg-quick-config is the Go configuration utility. wiresock-service handles the gateway’s traffic and supports NAT and proxy modes; the generated WireGuard tunnel is a separate service.
The first mode used conventional NAT. The service selected the default external interface and translated addresses for incoming and outgoing packets. It enabled Windows routing where it worked in my test setup and forwarded packets itself for the other connection types. Like Internet Connection Sharing, it shared an external connection, but allowed me to choose the client network’s address range.
Proxy mode is the default. It transparently redirects client TCP and UDP connections to local proxies, which open the outgoing connections on the gateway host. The service can use configured system HTTP/SOCKS5 proxy settings. DNS is handled separately: by default it forwards requests to local DNS servers when available, and the -dns service option sets preferred resolvers. The documented fallback is 8.8.8.8 and 1.1.1.1 when none are configured. Proxy mode does not forward external ICMP, so ping is not a useful test of external reachability here. Verify TCP, UDP and DNS paths independently.
This first version addressed the setup and routing goals I described above. If there was interest, I wanted to add:
- At the time of this v1.0.2.4 build, IPv6 was not supported.
- When an ISP does not assign a reachable public address, including behind carrier-grade NAT, an external relay or other reachable endpoint would be needed for this direct-inbound setup. I wanted to explore that.
- I wanted built-in DNS filtering similar to Pi-hole, without a separate Linux instance.
- I also wanted a UI to monitor connected users and assign access rules or bandwidth limits.