
WireSock VPN Gateway NAT Problem
Tagged: nat
- This topic has 11 replies, 2 voices, and was last updated 3 years, 6 months ago by
pikacu222.
-
AuthorPosts
-
April 5, 2023 at 3:29 pm #12946
pikacu222
ParticipantHello all,
I am trying to reach my local client but I cannot make it work somehow. There is no problem with VPN network. I can ping VPN IPs without a problem between VPN Gateway Server and VPN Client PC. Also when I check traceroute mylocalclientIP from VPN Client PC it routes packets to Wireguard + Wiresock VPN Gateway Server, so i think there is no problem with that I guess. I suspect “Force routing DISABLED!” log line.You can find some information about my setup below:
Any help much appreciated 🙂
April 5, 2023 at 5:52 pm #12947ParticipantLocal Client PC <—> Wireguard + Wiresock VPN Gateway Server —> VPN Client PC
April 5, 2023 at 5:54 pm #12948Participant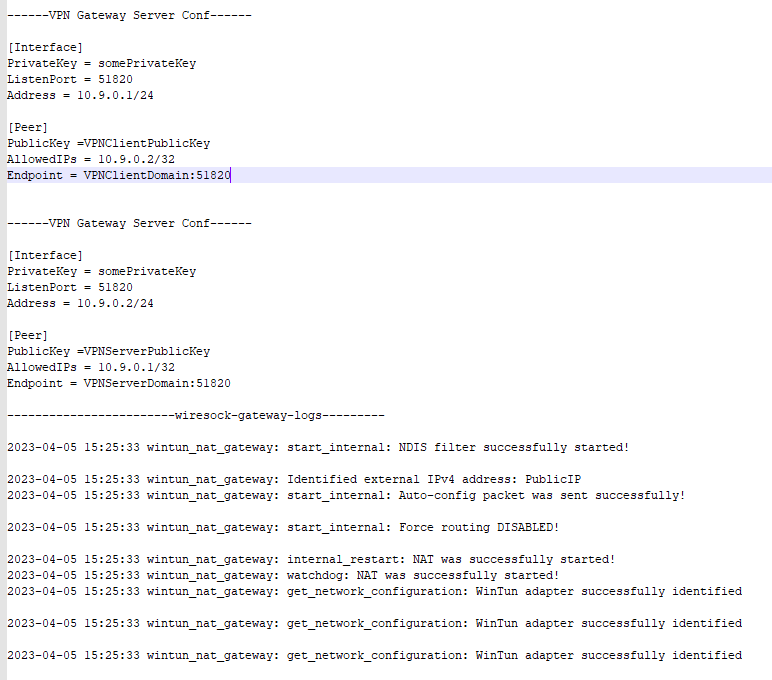 April 5, 2023 at 5:54 pm #12949Participant
Sorry for the mess. I could not send all the information in one post.
Thanks in advance
April 6, 2023 at 7:37 am #12957Vadim Smirnov
KeymasterThe message “Force routing DISABLED!” simply indicates that manual routing is not required for the internet interface in this case. While manual routing is necessary for some types of WAN connections, in this situation, the routing will be managed by the Windows TCP/IP stack.
In practice, the VPN Gateway implements Network Address Translation (NAT) from the WinTun/Wireguard virtual network adapter to the external network. This NAT functionality is unidirectional, meaning that a Wireguard client can access external resources, but an external host cannot establish a connection to the Wireguard client. If you encounter issues with VPN client communications, it is recommended to check the Windows Firewall settings to ensure proper connectivity.
April 6, 2023 at 7:53 am #12958ParticipantThank you for your replu. There is no problem with VPN connection actually. Wireguard + Wiresock VPN Gateway Server —> (Wireguard) VPN Client PC can communicate via their VPN IPs without problem. However, when I try to reach LAN behind the Wiresock VPN Gateway Server, it does not route to local network.
April 6, 2023 at 7:53 am #12959ParticipantThank you for your replu. There is no problem with VPN connection actually. Wireguard + Wiresock VPN Gateway Server —> (Wireguard) VPN Client PC can communicate via their VPN IPs without problem. However, when I try to reach LAN behind the Wiresock VPN Gateway Server, it does not route to local network.
April 6, 2023 at 7:53 am #12960ParticipantThank you for your replu. There is no problem with VPN connection actually. Wireguard + Wiresock VPN Gateway Server —> (Wireguard) VPN Client PC can communicate via their VPN IPs without problem. However, when I try to reach LAN behind the Wiresock VPN Gateway Server, it does not route to local network.
April 6, 2023 at 8:07 am #12961KeymasterHowever, when I try to reach LAN behind the Wiresock VPN Gateway Server, it does not route to local network.
NAT, or Network Address Translation, operates in a unidirectional manner. This means that it is not designed to route packets from the external interface to the internal network unless the connections associated with these packets were originally established from within the internal network. In other words, NAT allows internal devices to communicate with external networks, while simultaneously providing a layer of security by preventing unsolicited incoming traffic from directly accessing the internal network.
April 6, 2023 at 10:38 am #12962ParticipantHello Vadim,
When I read “WireSock VPN Gateway sets up a WireGuard VPN Server on Windows and allows WireGuard clients to connect to the server’s Internet/LAN” part, I thought it also route packets. What I understand is now, there is no such functionality. It only provides NAT. Is that correct or is there I way for it?
Thank you so much for your responses.
April 6, 2023 at 11:30 am #12963Keymasterallows WireGuard clients to connect to the server’s Internet/LAN
That’s correct; Wireguard clients can access the server’s Internet/LAN, but the reverse direction is not supported. In other words, it is not possible to access Wireguard clients via the server’s public interface. This limitation arises because, in order to establish a connection with a Wireguard client through the server’s public interface, a peer would need to know the client’s internal IP address. However, the client’s internal IP is not publicly known or advertised, which makes direct access to Wireguard clients unfeasible in this configuration.
While it is technically possible to map selected TCP/UDP ports on the external interface to Wireguard clients, the current version of WireSock VPN Gateway does not support port forwarding. This means that, as of now, direct access to Wireguard clients through the server’s public interface remains unfeasible using WireSock VPN Gateway.
April 6, 2023 at 4:24 pm #12964ParticipantThank you so much for the clarification 🙂
-
AuthorPosts
- You must be logged in to reply to this topic.